Understanding Cloud Provider Shared Responsibility Models: A Comprehensive Guide
September 25, 2026
How Cloud Compliance Frameworks Align with Industry Regulations
September 25, 2026
The Complete Guide to Data Processing Agreements for Cloud Infrastructure Services
In the era of digital transformation, organizations increasingly rely on cloud infrastructure services to manage and process their data. However, with this reliance comes the critical need for robust legal frameworks that govern data handling practices. A Data Processing Agreement (DPA) is essential for any organization utilizing cloud services, ensuring compliance with data protection regulations and safeguarding sensitive information. This comprehensive guide will explore what DPAs are, their importance in cloud infrastructure services, and how to effectively implement them.
What is a Data Processing Agreement?
A Data Processing Agreement (DPA) is a legally binding document that outlines the obligations and rights of parties involved in the processing of personal data. Typically, this agreement is established between a data controller (the entity that decides how and why personal data is processed) and a data processor (the entity that processes data on behalf of the controller). In the context of cloud infrastructure services, the cloud provider usually acts as the data processor.
DPAs are crucial for ensuring compliance with various data protection regulations, such as the General Data Protection Regulation (GDPR) in Europe, which mandates that data controllers must have a written agreement in place with their processors. This agreement must detail how personal data will be processed, the purpose of processing, and the security measures that will be implemented to protect the data.
Importance of DPAs in Cloud Services
Understanding the importance of DPAs in cloud services is essential for organizations looking to protect their data and comply with legal requirements. Here are several reasons why DPAs are vital:
- Legal Compliance: As mentioned, many data protection regulations require organizations to have DPAs in place. Non-compliance can lead to significant fines and legal repercussions.
- Data Security: DPAs typically outline specific security measures that the data processor must implement to protect sensitive information, thus ensuring a higher level of data security.
- Clear Responsibilities: A well-structured DPA clearly delineates the responsibilities of both parties, minimizing the risk of misunderstandings and disputes.
- Data Breach Protocol: DPAs often include clauses about data breach notifications, ensuring that data controllers are informed promptly in case of a data breach.
- Accountability: DPAs establish accountability for data handling practices, which is essential for maintaining trust with customers and stakeholders.
Key Elements of a Data Processing Agreement
When drafting a DPA, several key elements must be included to ensure that it meets legal standards and adequately protects both parties. Here are the essential components:
1. Definitions
Clearly define key terms used in the agreement, such as ‘personal data,’ ‘processing,’ and ‘data subject.’ This section sets the foundation for understanding the agreement.
2. Purpose of Processing
Specify the purpose for which the data will be processed. This helps ensure that the data processor does not use the data for any unauthorized purposes.
3. Duration of Processing
Indicate how long the data will be processed and the conditions under which it will be deleted or returned to the data controller.
4. Security Measures
Detail the security measures that the data processor must implement to protect personal data. This could include technical measures like encryption and organizational measures like employee training.
5. Sub-processors
If the data processor intends to engage sub-processors, the DPA must specify this and outline the conditions under which sub-processors can be engaged.
6. Data Subject Rights
Address how the data processor will assist the data controller in fulfilling its obligations regarding data subject rights, such as access, rectification, and erasure.
7. Data Breach Notification
Include provisions for the data processor to notify the data controller in the event of a data breach, along with the timeline and process for notification.
8. Liability and Indemnification
Outline the liability of each party in case of a breach of the DPA and the indemnification obligations that arise from such breaches.
9. Governing Law
Specify the governing law that will apply to the DPA, which is especially important for international agreements.
How to Create an Effective Data Processing Agreement
Creating an effective DPA requires careful consideration and attention to detail. Here is a step-by-step guide to drafting a robust agreement:
- Identify the Parties: Clearly identify the data controller and data processor, including their legal names and contact information.
- Gather Requirements: Understand the specific legal requirements applicable to your industry and jurisdiction. For instance, organizations operating in the EU must comply with GDPR.
- Draft the Agreement: Use a template or draft the DPA from scratch, ensuring that all key elements discussed above are included.
- Consult Legal Experts: Have legal experts review the DPA to ensure it meets all regulatory requirements and adequately protects your interests.
- Negotiate Terms: Discuss and negotiate terms with the data processor, ensuring both parties are in agreement on key aspects of the DPA.
- Finalize and Sign: Once both parties agree to the terms, finalize the document and sign it to make it legally binding.
- Regular Review: Regularly review and update the DPA as necessary, especially when there are changes in laws or business practices.
Common Mistakes to Avoid in DPAs
When drafting or reviewing a DPA, there are several common pitfalls that organizations should avoid:
- Vague Language: Avoid vague terms and ambiguous language that could lead to misunderstandings.
- Neglecting Compliance Requirements: Ensure that the DPA complies with all applicable regulations, such as GDPR or HIPAA.
- Inadequate Security Measures: Failing to specify appropriate security measures can expose your organization to risks.
- Ignoring Data Subject Rights: Ensure that the DPA addresses data subject rights and how the data processor will assist in fulfilling these obligations.
- Overlooking Sub-processor Clauses: If sub-processors will be used, clearly outline the terms under which they can be engaged.
Best Practices for Managing Data Processing Agreements
To effectively manage DPAs, organizations should consider the following best practices:
- Maintain a Central Repository: Keep all DPAs in a central location for easy access and management.
- Regular Audits: Conduct regular audits of DPAs to ensure compliance with legal requirements and internal policies.
- Training and Awareness: Provide training for employees on the importance of DPAs and how to manage them effectively.
- Establish Clear Communication: Ensure open lines of communication with data processors regarding any changes or issues related to the DPA.
Conclusion
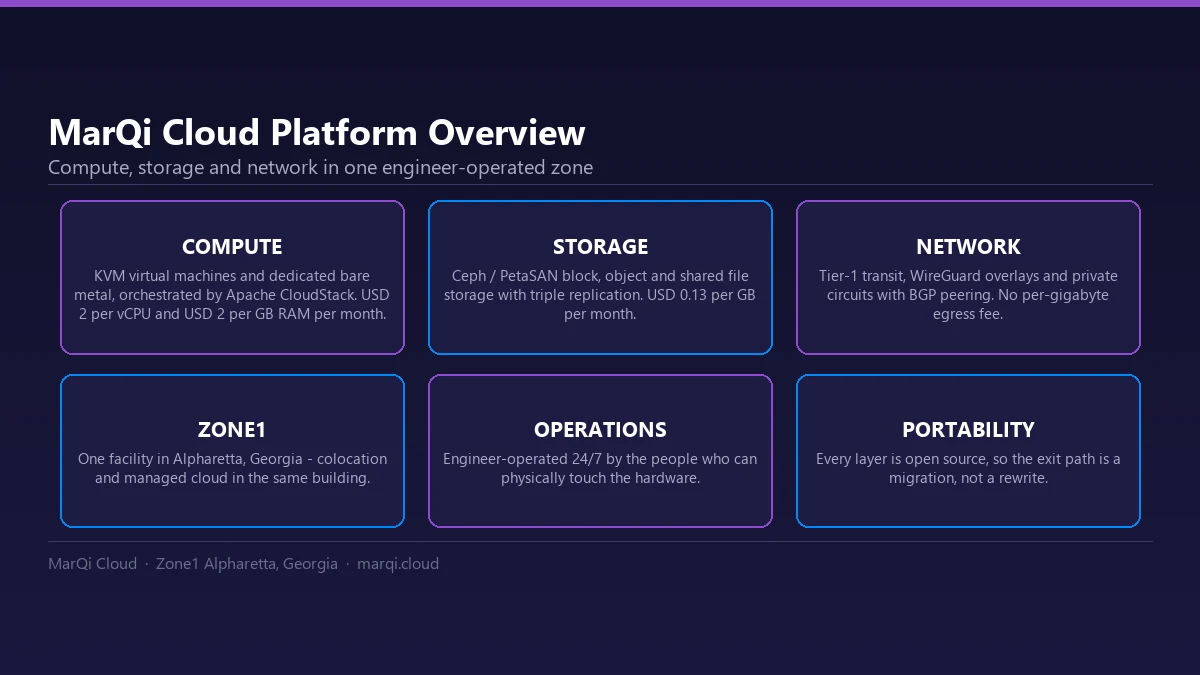
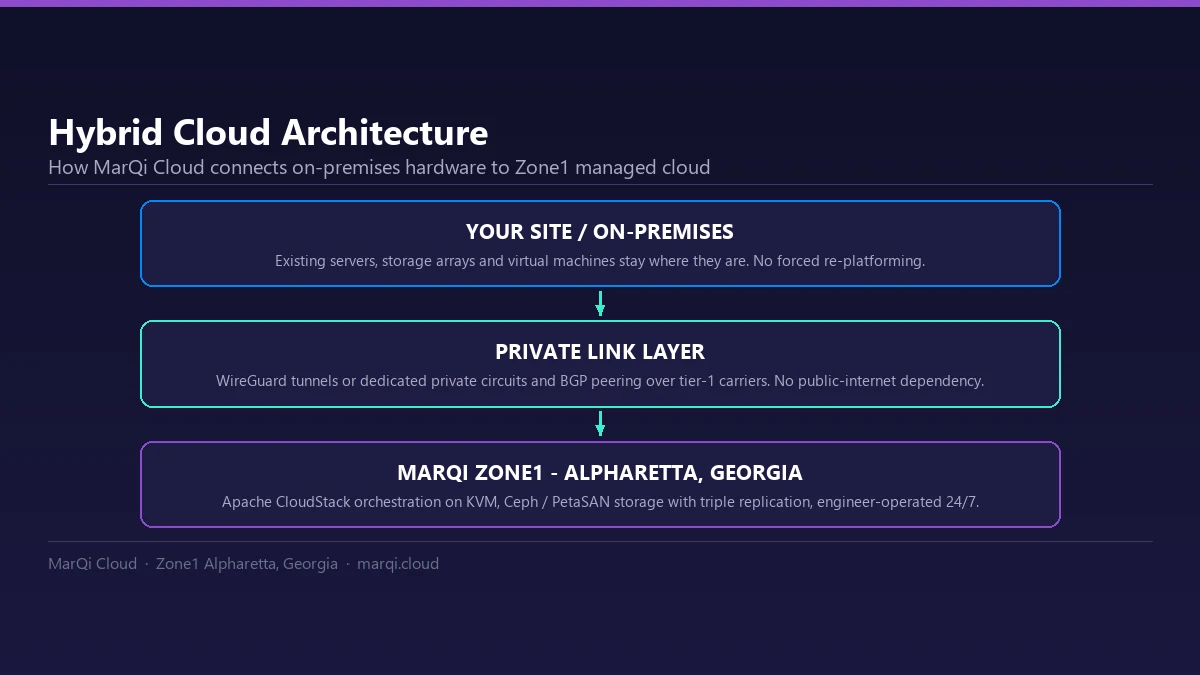
Data Processing Agreements are a critical component of cloud infrastructure services, ensuring compliance and protecting sensitive data. By understanding the importance of DPAs, knowing their key elements, and following best practices for management, organizations can safeguard their data while fostering trust with their customers. MarQi Cloud runs hybrid cloud and private hosting from its Zone1 data center in Alpharetta, Georgia, and its own Data Processing Addendum sets out the security measures, subprocessor terms and breach notification it commits to. For more information on how we can assist your organization, contact us today.
FAQ
1. What is the purpose of a Data Processing Agreement?
The purpose of a Data Processing Agreement is to establish the obligations and rights of parties involved in the processing of personal data, ensuring compliance with data protection regulations.
2. Who needs a Data Processing Agreement?
Any organization that processes personal data, especially those using third-party cloud services, needs a Data Processing Agreement to comply with legal requirements.
3. What are the key elements of a DPA?
Key elements of a DPA include definitions, purpose of processing, duration of processing, security measures, data subject rights, and breach notification procedures.
4. How often should a DPA be reviewed?
A DPA should be reviewed regularly, especially when there are changes in data protection laws or organizational practices.
5. What happens if a DPA is not in place?
If a DPA is not in place, organizations may face legal penalties, fines, and increased risks of data breaches.
6. Can a DPA be modified after it is signed?
Yes, a DPA can be modified after it is signed, but both parties must agree to the changes, and documentation should be updated accordingly.
7. What should be done in case of a data breach?
In the event of a data breach, the data processor must notify the data controller as specified in the DPA, detailing the nature of the breach and the data affected.
8. How can organizations ensure compliance with DPAs?
Organizations can ensure compliance with DPAs by conducting regular audits, providing employee training, and maintaining clear communication with data processors.