The Complete Guide to Cloud Operations Maturity Models for Enterprise IT
September 23, 2026
The Complete Guide to SOC 2 Type II Compliance on Cloud Infrastructure
September 23, 2026
How to Design Cloud Architecture for Regulatory Compliance from Day One
In today’s digital landscape, ensuring regulatory compliance from the outset of cloud architecture design is crucial for organizations aiming to protect sensitive data and avoid hefty penalties. As businesses increasingly migrate to the cloud, the need for robust compliance frameworks becomes more pronounced. This article provides an in-depth exploration of how to design cloud architecture that adheres to regulatory requirements from day one, emphasizing best practices, actionable insights, and the importance of choosing the right cloud provider.
Understanding Regulatory Compliance
Regulatory compliance refers to the adherence to laws, regulations, guidelines, and specifications relevant to an organization’s business processes. In the context of cloud computing, this can encompass various data protection laws, industry standards, and compliance frameworks. Non-compliance can lead to significant financial penalties, reputational damage, and operational disruptions, making it imperative for organizations to embed compliance into their cloud architecture from the beginning.
Key Regulatory Frameworks
Several regulatory frameworks govern how organizations manage and protect data in the cloud. Understanding these frameworks is essential for designing compliant cloud architecture. Some of the most relevant include:
- General Data Protection Regulation (GDPR): This European Union regulation mandates strict guidelines for the collection and processing of personal information.
- Health Insurance Portability and Accountability Act (HIPAA): In the healthcare sector, HIPAA sets standards for the protection of patient health information.
- Payment Card Industry Data Security Standard (PCI DSS): This standard is crucial for organizations that handle credit card transactions, ensuring secure data transmission and storage.
- Federal Risk and Authorization Management Program (FedRAMP): This U.S. government program ensures that cloud services used by federal agencies meet stringent security requirements.
Each of these frameworks has specific requirements that must be integrated into cloud architecture design. For example, GDPR emphasizes data encryption and user consent, while HIPAA focuses on safeguarding protected health information (PHI).
Designing Cloud Architecture for Compliance
Designing cloud architecture for regulatory compliance involves several critical steps:
1. Conduct a Compliance Assessment
Before embarking on cloud architecture design, conduct a thorough compliance assessment to identify relevant regulations applicable to your business. This assessment should include a review of:
- Industry-specific regulations
- Data types and sensitivity
- Geographic data residency requirements
By understanding these factors, you can tailor your cloud architecture design to meet specific compliance needs.
2. Choose the Right Cloud Deployment Model
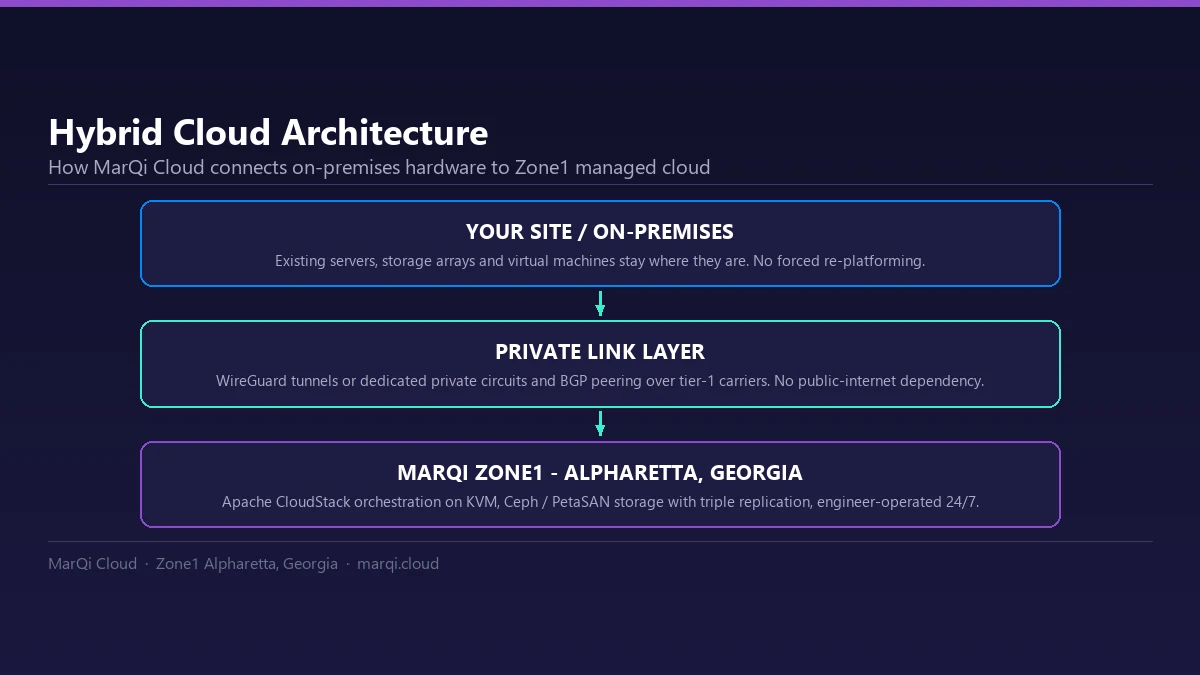
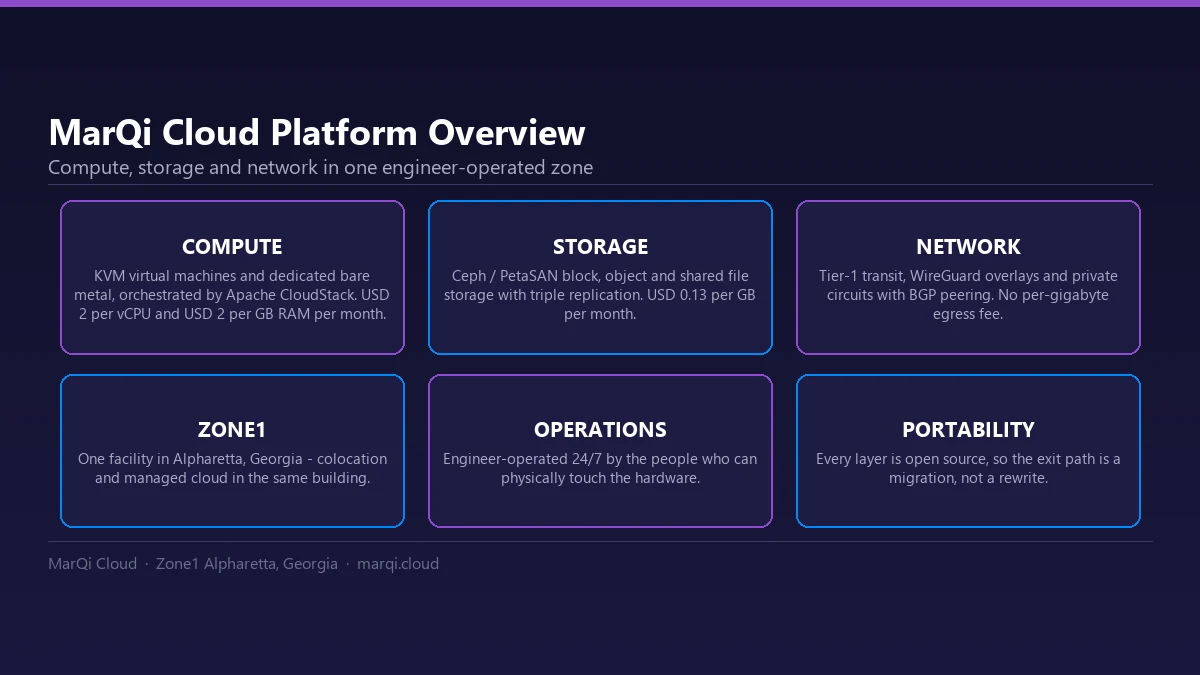
Selecting an appropriate cloud deployment model—public, private, or hybrid—is essential for compliance. For instance, organizations handling sensitive data may opt for private cloud solutions to maintain greater control over data security and compliance. MarQi Cloud’s hybrid cloud lets you keep sensitive workloads on dedicated private infrastructure while other workloads run elsewhere; the platform supplies infrastructure controls, and your organization still evidences its own compliance.
3. Implement Data Encryption
Data encryption is a fundamental aspect of compliance. Ensure that all data, both at rest and in transit, is encrypted using industry-standard protocols. This protects sensitive information and mitigates risks associated with data breaches. Utilize encryption technologies such as AES-256 for data encryption and TLS for secure data transmission.
4. Establish Identity and Access Management (IAM)
Implementing a robust IAM system is crucial for controlling access to sensitive data. Ensure that only authorized personnel have access to specific data and resources. Use multi-factor authentication (MFA) and role-based access controls (RBAC) to enhance security and compliance.
5. Monitor and Audit Compliance
Continuous monitoring and auditing are vital for maintaining compliance. Implement logging and monitoring solutions that track access and changes to sensitive data. Regular audits should be conducted to ensure compliance with regulatory standards. MarQi’s Status & Monitoring page reports the health of the platform itself; tracking the compliance status of your own workloads still requires your own logging and audit tooling.
Best Practices for Cloud Compliance
To effectively design cloud architecture for compliance, consider the following best practices:
- Document Everything: Maintain comprehensive documentation of compliance policies, procedures, and architecture designs. This documentation will be invaluable during audits and assessments.
- Engage with Legal and Compliance Teams: Involve legal and compliance experts in the design process to ensure that all regulatory requirements are addressed.
- Utilize Compliance Frameworks: Leverage established compliance frameworks and best practices as a foundation for your cloud architecture design. Frameworks such as NIST Cybersecurity Framework and ISO 27001 can provide valuable guidance.
- Stay Updated: Regulatory requirements are constantly evolving. Stay informed about changes in regulations and adapt your cloud architecture accordingly.
Example Scenarios: Compliance by Design
The scenarios below are illustrative examples of how the practices in this guide are typically applied; they are not reports from specific organizations or MarQi Cloud customers.
1. Healthcare Organization
A healthcare provider moving patient data to a private cloud can start with a compliance assessment and map HIPAA Security Rule safeguards, such as access controls, audit controls and transmission security, into the architecture before any data is migrated.
2. Financial Institution
A fintech startup that handles payment card data can define its cardholder data environment and the PCI DSS requirements that apply to it on day one, designing encryption and identity and access management into the platform instead of adding them later.
Common Mistakes to Avoid
When designing cloud architecture for compliance, organizations often make several common mistakes:
- Neglecting Compliance Assessment: Failing to conduct a comprehensive compliance assessment can lead to oversight of critical regulations.
- Choosing the Wrong Cloud Provider: Selecting a cloud provider that does not prioritize compliance can jeopardize your organization’s ability to meet regulatory requirements. Ensure that your chosen provider offers enterprise-grade cloud infrastructure designed for compliance.
- Inadequate Documentation: Poor documentation can hinder compliance audits and assessments, making it essential to maintain detailed records.
Frequently Asked Questions
What is regulatory compliance in cloud computing?
Regulatory compliance in cloud computing refers to adhering to laws, regulations, and standards governing data protection and management in cloud environments.
Why is compliance important for cloud architecture?
Compliance is crucial for protecting sensitive data, avoiding legal penalties, and maintaining customer trust, especially for organizations in regulated industries.
How can I ensure my cloud architecture is compliant?
To ensure compliance, conduct a thorough assessment, choose the right cloud provider, implement data encryption, and establish robust access controls.
What are some common compliance frameworks?
Common compliance frameworks include GDPR, HIPAA, PCI DSS, and FedRAMP, each with specific requirements for data protection and management.
How often should I audit my cloud compliance?
Regular audits should be conducted at least annually or whenever significant changes are made to your cloud architecture or regulatory environment.
What role does data encryption play in compliance?
Data encryption is essential for protecting sensitive information and is often a requirement under many regulatory frameworks.
Can I use a public cloud for sensitive data?
Yes, but it’s crucial to implement strong security measures and ensure that the public cloud provider meets compliance requirements relevant to your industry.
How can MarQi Cloud help with compliance?
MarQi Cloud provides the infrastructure layer, such as private cloud environments on isolated networks, on which your own controls are built. MarQi Cloud does not claim compliance certifications such as SOC 2, ISO 27001, HIPAA, PCI DSS or FedRAMP; your organization evidences its own compliance.
What is the cost of compliance in cloud services?
The cost of compliance varies based on industry requirements, the complexity of your cloud architecture, and the cloud provider chosen. It’s important to factor in these costs during planning.
How do I choose a compliant cloud provider?
When choosing a cloud provider, assess their compliance certifications, data protection measures, and track record in meeting regulatory requirements.
What happens if I fail to comply?
Failing to comply with regulatory requirements can result in severe penalties, legal action, and reputational damage, underscoring the importance of proactive compliance measures.
How can I integrate compliance into my DevOps process?
Integrating compliance into your DevOps process involves automating compliance checks, incorporating security into development workflows, and continuously monitoring for compliance adherence.
Conclusion
Designing cloud architecture for regulatory compliance from day one is not only a best practice but a necessity in today’s data-driven world. By understanding relevant regulations, implementing robust security measures, and choosing a cloud provider whose controls fit their requirements, organizations can safeguard sensitive data and support their compliance obligations. Start your cloud journey with confidence by embedding compliance into your design process, and set the foundation for a secure and successful cloud environment.