The Ultimate Guide for IT Compliance Officers: Cloud Audit Preparation & Evidence Collection
September 24, 2026
Why HITRUST CSF Certification Signals Healthcare Cloud Security Maturity
September 24, 2026
How PCI DSS Level 1 Compliance Protects Cardholder Data in the Cloud
In today’s digital landscape, safeguarding sensitive information is paramount, particularly for organizations that handle cardholder data. Achieving PCI DSS Level 1 compliance is not just a regulatory requirement; it is a critical component of building trust with customers and safeguarding your enterprise’s reputation. This comprehensive guide will explore how PCI DSS Level 1 compliance on cloud infrastructure protects cardholder data, ensuring your organization remains secure against evolving threats while maximizing the benefits of cloud technologies.
What is PCI DSS?
The Payment Card Industry Data Security Standard (PCI DSS) is a set of security standards designed to ensure that organizations that handle credit card information maintain a secure environment. Developed by the Payment Card Industry Security Standards Council (PCI SSC), PCI DSS outlines specific requirements aimed at protecting cardholder data and minimizing the risk of data breaches. Compliance with these standards is essential for any organization that processes, stores, or transmits cardholder data.
Understanding PCI DSS Level 1
PCI DSS Level 1 is the highest level of compliance, applicable to organizations that process over 6 million transactions annually. This level mandates rigorous security measures, including:
- Annual on-site assessments by a Qualified Security Assessor (QSA)
- Regular penetration testing and vulnerability assessments
- Implementing a comprehensive security program
Organizations achieving Level 1 compliance demonstrate a commitment to protecting cardholder data through stringent security practices. This is particularly important for enterprises leveraging cloud infrastructure, as compliance ensures that data remains secure even in a shared environment.
The Importance of PCI DSS Level 1 Compliance
Achieving PCI DSS Level 1 compliance offers numerous benefits, including:
- Enhanced Security: Compliance ensures that your organization employs the highest security measures, reducing the risk of data breaches.
- Customer Trust: Being PCI DSS compliant helps build customer confidence, as they know their cardholder data is handled securely.
- Legal Protection: Compliance can provide legal protection in case of a data breach, demonstrating that the organization took necessary steps to protect sensitive information.
For organizations utilizing cloud services, compliance is crucial for ensuring that the cloud provider meets stringent security standards, protecting cardholder data throughout its lifecycle.
How PCI DSS Compliance Protects Cardholder Data
PCI DSS compliance provides a framework for protecting cardholder data through various security measures, including:
1. Strong Access Control Measures
Ensuring that only authorized personnel have access to cardholder data is vital. PCI DSS mandates robust access control policies, including:
- Unique user IDs for each individual with computer access to cardholder data
- Restricting access based on the need to know
- Regular reviews of access logs
2. Encryption of Data
Encryption is a fundamental aspect of PCI DSS compliance. It protects cardholder data both at rest and in transit, making it unreadable to unauthorized users. This is especially important for organizations using cloud infrastructure, as data may be transmitted across various networks.
3. Regular Security Testing
PCI DSS requires regular security testing to identify vulnerabilities and ensure the effectiveness of security measures. This includes:
- Annual penetration tests
- Quarterly vulnerability scans
4. Maintaining a Secure Network
Organizations must maintain a secure network by implementing firewalls, secure configurations, and regularly updating security patches. This is crucial for protecting cardholder data from external threats.
5. Monitoring and Testing Networks
Continuous monitoring of networks and systems is essential for detecting and responding to security incidents. PCI DSS requires organizations to:
- Implement logging mechanisms
- Regularly review logs for suspicious activity
Cloud Infrastructure and PCI DSS Compliance
As more businesses migrate to cloud infrastructure, understanding how PCI DSS compliance applies in this context is essential. Cloud providers must also be PCI DSS compliant, ensuring that they adhere to the same security standards as their clients.
The Role of Cloud Providers
Cloud service providers (CSPs) play a crucial role in PCI DSS compliance. They must implement security measures that protect cardholder data while ensuring that clients can meet their compliance requirements. Key considerations include:
- Data encryption during storage and transmission
- Access controls to restrict unauthorized access
- Regular security assessments and audits
Benefits of Using PCI DSS-Compliant Cloud Infrastructure
Utilizing PCI DSS-compliant cloud infrastructure can provide several advantages:
- Scalability: Cloud solutions can easily scale to accommodate growing transaction volumes while maintaining compliance.
- Cost-Effectiveness: Leveraging cloud infrastructure can reduce the costs associated with maintaining on-premises solutions.
- Expert Support: Many cloud providers offer expert support to help organizations navigate compliance challenges.
Steps to Achieve PCI DSS Level 1 Compliance
Achieving PCI DSS Level 1 compliance involves a series of steps:
- Assess Your Current Environment: Conduct a thorough assessment of your current systems and processes to identify gaps in compliance.
- Implement Required Security Measures: Develop and implement security measures that align with PCI DSS requirements.
- Engage a Qualified Security Assessor: Partner with a QSA to guide you through the compliance process and conduct necessary assessments.
- Complete Documentation: Ensure all required documentation is completed and maintained for compliance audits.
- Conduct Regular Reviews: Continuously review and update security measures to maintain compliance.
Common Challenges in Achieving Compliance
Organizations may encounter several challenges when striving for PCI DSS Level 1 compliance, such as:
- Complexity of Requirements: Understanding and implementing the comprehensive requirements can be daunting.
- Resource Constraints: Many organizations lack the necessary resources or expertise to achieve compliance effectively.
- Maintaining Compliance: Compliance is not a one-time effort; ongoing monitoring and updates are required to maintain standards.
Conclusion
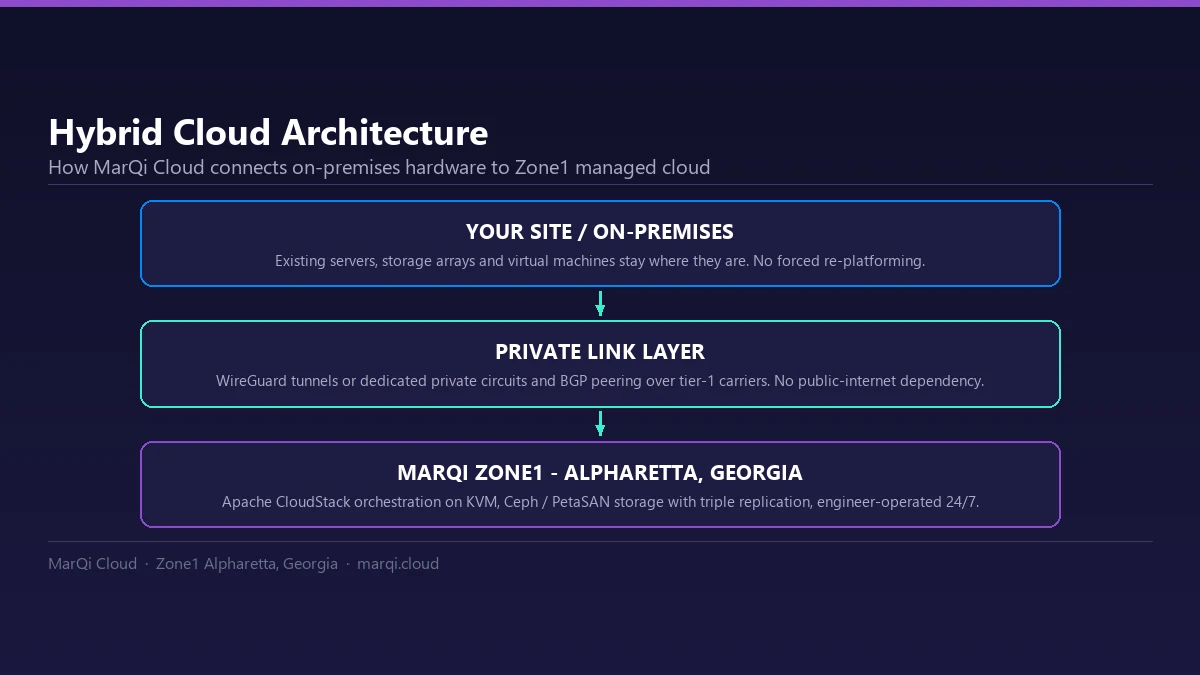
Achieving PCI DSS Level 1 compliance is essential for organizations that handle cardholder data, particularly those utilizing cloud infrastructure. By understanding the requirements and implementing robust security measures, businesses can protect sensitive information, build customer trust, and minimize the risk of data breaches. For organizations handling cardholder data, MarQi Cloud offers private infrastructure in its Zone1 data center in Alpharetta, Georgia; it does not claim PCI DSS certification, and your organization evidences its own compliance. Explore our Hybrid Cloud Solutions to learn more about how we can help you achieve PCI DSS compliance.
FAQs
1. What is PCI DSS Level 1 compliance?
PCI DSS Level 1 compliance applies to organizations that process over 6 million card transactions annually and requires stringent security measures.
2. Why is PCI DSS compliance important?
Compliance is crucial for protecting cardholder data, building customer trust, and minimizing legal liabilities in the event of a data breach.
3. How can cloud infrastructure be PCI DSS compliant?
Cloud providers must implement security measures, such as encryption and access controls, to ensure compliance with PCI DSS standards.
4. What are the consequences of non-compliance?
Non-compliance can result in heavy fines, legal liabilities, and damage to an organization’s reputation.
5. How often must organizations assess their PCI DSS compliance?
Organizations are required to conduct annual assessments and continuous monitoring to ensure ongoing compliance.
6. What is the role of a Qualified Security Assessor (QSA)?
A QSA is a certified professional who helps organizations navigate the compliance process and conduct necessary assessments.
7. Can small businesses achieve PCI DSS Level 1 compliance?
While challenging, small businesses can achieve compliance by following guidelines and seeking assistance from qualified professionals.
8. What security measures are required for PCI DSS compliance?
Required measures include strong access controls, data encryption, regular security testing, and maintaining a secure network.