How Cloud Compliance Frameworks Align with Industry Regulations
September 25, 2026
The Complete Guide to Cloud Security Questionnaire Responses for Enterprise Procurement
September 26, 2026
Why Audit-Ready Cloud Infrastructure Documentation Simplifies Compliance Reviews
In today’s digital landscape, where data compliance and security are paramount, organizations must prioritize audit-ready cloud infrastructure documentation. This comprehensive approach not only streamlines compliance reviews but also enhances overall operational efficiency. In this article, we will explore the critical importance of maintaining thorough documentation within cloud infrastructures and how it can significantly simplify compliance audits. You will learn about best practices, the role of documentation in various compliance frameworks, and how to align your cloud strategy with regulatory requirements.
Understanding Audit-Ready Documentation
Audit-ready documentation refers to the systematic organization and maintenance of all relevant records, policies, and procedures that support an organization’s compliance with industry regulations and standards. This documentation serves as a roadmap for auditors, providing them with the necessary information to assess compliance effectively. In the context of cloud infrastructure, audit-ready documentation includes:
- Configuration Management Records: Detailed descriptions of the cloud infrastructure setup, including network configurations, server setups, and software installations.
- Change Management Logs: Records of any changes made to the cloud infrastructure, including updates, patches, and configuration changes.
- Access Control Policies: Documentation of user access levels, permissions granted, and any changes to access controls.
- Incident Response Plans: Procedures for responding to security incidents, including roles and responsibilities and communication plans.
- Compliance Certifications: Documentation of any certifications that demonstrate compliance with industry standards, such as ISO 27001 or HIPAA.
By maintaining thorough audit-ready documentation, organizations can demonstrate due diligence and readiness for compliance reviews, ultimately leading to smoother audits.
The Importance of Compliance Reviews
Compliance reviews are essential for ensuring that organizations adhere to regulatory requirements and best practices. These reviews help mitigate risks, enhance data security, and build trust with clients and stakeholders. The significance of compliance reviews can be summarized as follows:
- Risk Management: Regular compliance reviews help identify potential risks and vulnerabilities within the cloud infrastructure, enabling organizations to take proactive measures.
- Legal Obligations: Many industries are subject to strict regulatory requirements. Compliance reviews ensure organizations meet these obligations, avoiding potential legal issues.
- Enhanced Security: Through compliance reviews, organizations can identify security gaps and implement necessary controls to protect sensitive data.
- Improved Trust: Demonstrating compliance fosters trust among clients, partners, and stakeholders, which is crucial for business success.
In the realm of cloud infrastructure, the importance of compliance reviews cannot be overstated. As organizations migrate to cloud solutions, the need for robust compliance frameworks becomes even more critical.
Key Elements of Audit-Ready Documentation
Creating effective audit-ready documentation requires a comprehensive understanding of the key elements that will be scrutinized during compliance reviews. Below are the critical components to consider:
1. Policies and Procedures
Documenting clear policies and procedures is fundamental to compliance. This includes:
- Data governance policies
- Security protocols
- Incident response procedures
2. Access Control Records
Maintaining records of who has access to what is crucial for demonstrating compliance with standards such as GDPR or HIPAA. This includes:
- User access logs
- Change logs for access privileges
3. Audit Trails
Comprehensive audit trails provide a detailed account of all actions taken within the cloud infrastructure. This includes:
- System logs
- Change management records
4. Compliance Mapping
Mapping your documentation to specific compliance requirements helps streamline the audit process. This includes:
- Mapping controls to specific regulations
- Documenting evidence of compliance
5. Training and Awareness Programs
Keeping staff informed and trained on compliance requirements is essential. This includes:
- Regular training sessions
- Documentation of training completion
Benefits of Audit-Ready Documentation
Maintaining audit-ready documentation offers a multitude of benefits for organizations, particularly in the context of cloud infrastructure:
1. Streamlined Compliance Audits
With comprehensive documentation, auditors can quickly access relevant information, reducing the time and effort required for compliance reviews.
2. Enhanced Security Posture
Thorough documentation helps identify security vulnerabilities and strengthen the overall security posture of the organization.
3. Improved Operational Efficiency
Clear documentation processes reduce redundancies and improve collaboration among teams, leading to enhanced operational efficiency.
4. Increased Accountability
Documenting roles and responsibilities fosters accountability among team members, ensuring compliance efforts are taken seriously.
5. Cost Savings
By mitigating compliance risks, organizations can save on potential fines, penalties, and remediation costs associated with non-compliance.
Best Practices for Creating Audit-Ready Documentation
To ensure your cloud infrastructure documentation is audit-ready, consider the following best practices:
1. Regular Updates and Reviews
Documentation should be regularly reviewed and updated to reflect changes in the infrastructure, policies, and compliance requirements.
2. Centralized Documentation Repository
Utilizing a centralized repository for documentation makes it easier to maintain and access critical records.
3. Use Clear and Consistent Language
Ensure that all documentation uses clear, concise language that is easily understandable by all stakeholders.
4. Implement Version Control
Version control helps track changes over time, providing a clear history of documentation updates.
5. Engage Stakeholders
Involve relevant stakeholders in the documentation process to ensure that all necessary information is captured.
How MarQi Cloud Supports Compliance Efforts
At MarQi Cloud, we understand the complexities of maintaining an audit-ready cloud infrastructure. Our enterprise-grade cloud solutions are designed with compliance in mind, providing organizations with the tools they need to simplify compliance reviews. Our key offerings include:
- Hybrid Cloud Infrastructure: Our hybrid cloud solutions provide flexibility, with controls that support, but do not replace, your own compliance with industry regulations.
- Secure Hosting Solutions: We offer private and secure hosting environments that protect sensitive data and support compliance requirements.
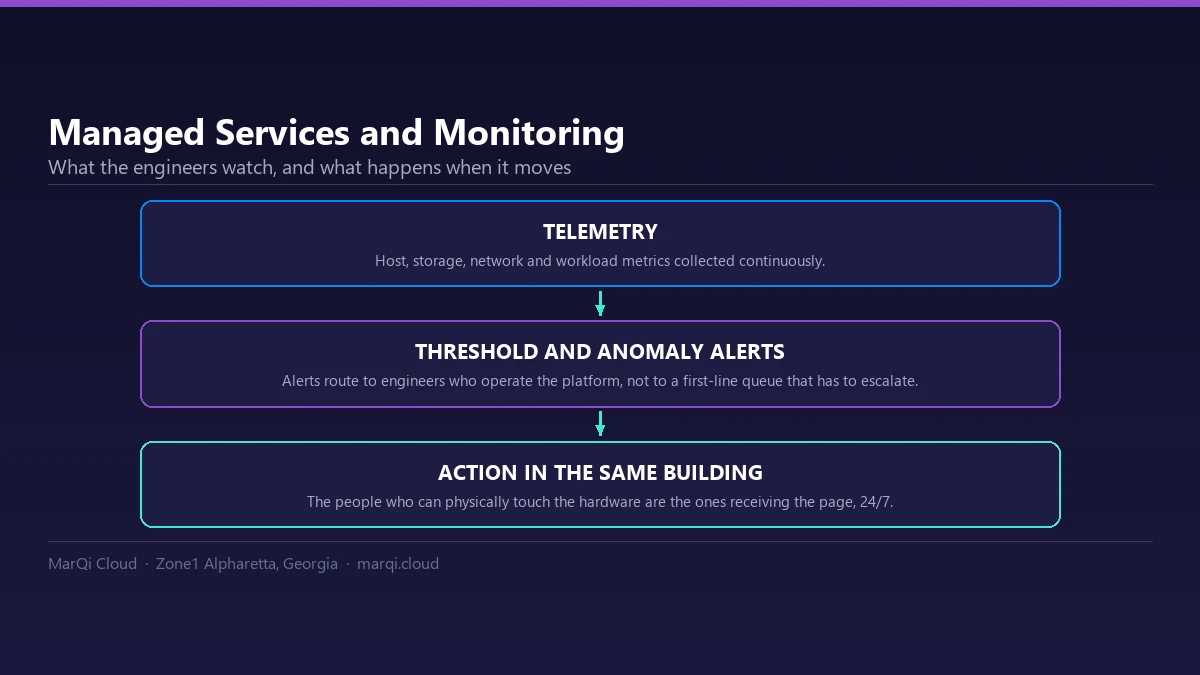
- Managed Services: Our white-glove managed services add 24/7 engineer-run operations and monitoring, so changes to your infrastructure are tracked as regulatory standards evolve; the compliance itself stays with your organization.
- Disaster Recovery Solutions: Our business continuity solutions help organizations maintain compliance even in the event of a disaster.
MarQi Cloud’s infrastructure and managed services supply controls that support, but do not replace, your organization’s own compliance work.
Conclusion
In conclusion, audit-ready cloud infrastructure documentation is essential for simplifying compliance reviews and enhancing overall operational efficiency. By maintaining thorough documentation, organizations can streamline compliance audits, improve security posture, and foster accountability among team members. As regulations continue to evolve, organizations must prioritize audit-ready documentation to ensure they remain compliant and competitive in the digital landscape. For more information on how MarQi Cloud can support your compliance efforts, contact us today.
Frequently Asked Questions
1. What is audit-ready documentation?
Audit-ready documentation refers to the organized maintenance of records, policies, and procedures that support compliance with industry regulations.
2. Why is compliance important?
Compliance is crucial for mitigating risks, ensuring legal obligations are met, and enhancing data security.
3. What are the key components of audit-ready documentation?
Key components include policies and procedures, access control records, audit trails, compliance mapping, and training documentation.
4. How can audit-ready documentation benefit my organization?
Benefits include streamlined compliance audits, enhanced security posture, improved operational efficiency, increased accountability, and cost savings.
5. What best practices should I follow for documentation?
Best practices include regular updates, centralized repositories, clear language, version control, and stakeholder engagement.
6. How does MarQi Cloud support compliance?
MarQi Cloud offers hybrid cloud infrastructure, secure hosting solutions, managed services, and disaster recovery solutions to support compliance efforts.
7. What are common compliance frameworks?
Common frameworks include GDPR, HIPAA, PCI-DSS, and ISO 27001.
8. How often should documentation be reviewed?
Documentation should be reviewed regularly, especially after significant changes to infrastructure, policies, or compliance requirements.