Mastering Container Orchestration: Managing Thousands of Microservices in the Cloud
October 6, 2026
The Complete Guide to Container Logging and Monitoring on Cloud Infrastructure
October 7, 2026
Why Sidecar Proxy Patterns Enhance Security and Observability in Cloud Containers
As organizations increasingly adopt cloud-native architectures, the need for enhanced security and observability becomes paramount. Sidecar proxy patterns have emerged as a robust solution for addressing these challenges in cloud container environments. In this comprehensive guide, we will explore how sidecar proxies enhance security, improve observability, and ultimately contribute to the operational excellence of cloud containers. By the end, you’ll understand the strategic advantages of implementing sidecar proxies and how they align with best practices for enterprise cloud solutions.
What is a Sidecar Proxy?
A sidecar proxy is a design pattern used in microservices architecture where a proxy server runs alongside an application service within the same container or pod. This pattern decouples the core application logic from the ancillary functionalities, such as security, monitoring, and networking. The sidecar proxy intercepts all inbound and outbound traffic, providing a dedicated layer for managing communication.
In cloud container environments, sidecar proxies are often deployed using orchestration tools like Kubernetes. This allows development teams to implement policies and controls without altering the application code itself. The sidecar pattern simplifies the management of microservices, ensuring that they are both resilient and secure.
Benefits of Sidecar Proxy Patterns
Integrating sidecar proxies into cloud container architectures offers numerous advantages:
- Decoupling: By separating the proxy functionality from the application, developers can focus on building features without worrying about networking concerns.
- Consistent Policies: Centralizing security and observability policies in the sidecar ensures uniform enforcement across all microservices.
- Scalability: Sidecar proxies can be deployed independently, allowing for scalable and flexible infrastructure.
- Enhanced Security: Sidecar proxies can manage authentication and encryption, reducing the attack surface of the application.
- Improved Observability: By capturing metrics and logs, sidecars provide deep insights into application performance.
Enhancing Security with Sidecar Proxies
Security is a top concern for enterprise cloud providers. Sidecar proxies significantly enhance security through various mechanisms:
1. Traffic Encryption
Sidecar proxies can enforce encryption protocols like TLS, ensuring that all data transmitted between services is secure. This is particularly important for applications that handle sensitive data, such as healthcare or financial services. According to the National Institute of Standards and Technology (NIST), implementing encryption is critical for protecting data integrity and confidentiality.
2. Service Authentication
Sidecar proxies can facilitate mutual TLS (mTLS) authentication, ensuring that only authorized services can communicate with each other. This prevents man-in-the-middle attacks and ensures that data is only exchanged between trusted entities.
3. Policy Enforcement
Security policies can be uniformly enforced across all services via the sidecar proxy. This includes rate limiting, access controls, and logging. By centralizing these policies, organizations can reduce configuration errors and enhance compliance.
4. Threat Detection
Sidecar proxies can incorporate advanced threat detection mechanisms, such as anomaly detection and intrusion detection systems (IDS). By monitoring traffic patterns, these proxies can identify potential threats in real time, enabling swift responses to security incidents.
To illustrate the impact of these security enhancements, consider the following comparison table:
| Security Feature | Without Sidecar Proxy | With Sidecar Proxy |
|---|---|---|
| Traffic Encryption | Application-level implementation | Uniform enforcement via proxy |
| Service Authentication | Manual certificate management | Automated mTLS setup |
| Policy Enforcement | Service-specific policies | Centralized policy management |
| Threat Detection | Limited visibility | Real-time monitoring and alerts |
Improving Observability with Sidecar Proxies
In addition to enhancing security, sidecar proxies play a crucial role in improving observability within cloud container environments:
1. Centralized Logging
Sidecar proxies can aggregate logs from multiple services, providing a centralized logging solution. This simplifies troubleshooting and enables teams to identify issues quickly. By integrating with logging platforms like ELK Stack or Splunk, organizations can gain comprehensive insights into application performance.
2. Metrics Collection
Sidecars can automatically collect metrics related to service performance, such as latency, error rates, and throughput. This data is invaluable for performance tuning and capacity planning. Tools like Prometheus can be used to visualize these metrics, giving teams a clear view of their application’s health.
3. Distributed Tracing
Implementing distributed tracing is essential for understanding complex microservices interactions. Sidecar proxies can inject tracing headers into requests, enabling tools like Jaeger or Zipkin to trace requests across services. This provides visibility into bottlenecks and performance issues.
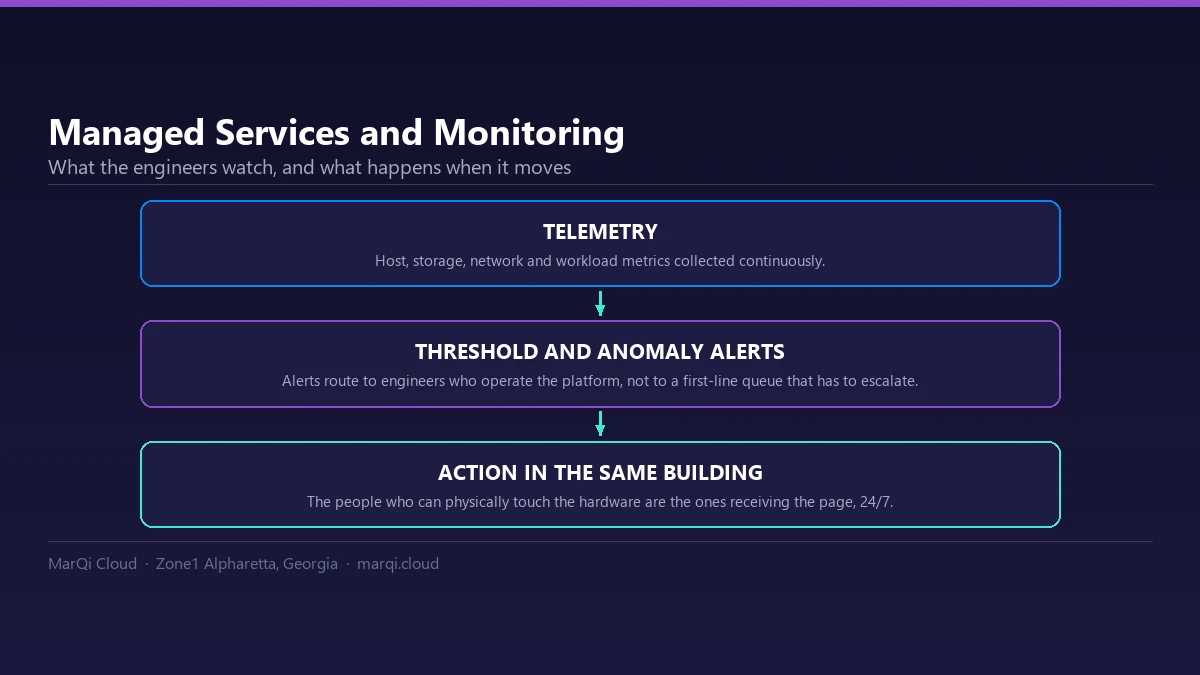
4. Alerting and Monitoring
By integrating with monitoring tools, sidecar proxies can trigger alerts based on predefined thresholds. This proactive approach allows teams to respond to potential issues before they impact users.
Sidecar Proxy Implementation Strategies
To effectively implement sidecar proxies in your cloud container architecture, consider the following strategies:
1. Choose the Right Proxy
Select a sidecar proxy that aligns with your specific use cases and requirements. Popular choices include Envoy, Istio, and Linkerd. Each offers unique features and capabilities, so evaluate them based on your architecture.
2. Define Security Policies
Establish clear security policies that will be enforced by the sidecar proxies. This includes authentication methods, encryption protocols, and access controls. Ensure that these policies are documented and communicated to all stakeholders.
3. Monitor Performance
Continuously monitor the performance of your sidecar proxies. Use metrics and logs to identify potential bottlenecks or failures. Regularly review and optimize the configurations to ensure optimal performance.
4. Incorporate CI/CD Practices
Integrate sidecar proxy deployments into your continuous integration and continuous deployment (CI/CD) pipelines. This ensures that updates and changes are rolled out seamlessly, reducing downtime and improving agility.
5. Provide Training and Documentation
Ensure that your development and operations teams are trained on the use of sidecar proxies. Provide comprehensive documentation that outlines best practices, troubleshooting steps, and common use cases.
Case Studies and Examples
Several organizations have successfully implemented sidecar proxies to enhance security and observability:
1. Financial Services Company
A leading financial services company adopted a sidecar proxy architecture to secure sensitive transactions. By implementing mTLS and centralized logging, they reduced security incidents by 40% and improved incident response times.
2. Healthcare Provider
A healthcare provider utilized sidecar proxies to comply with HIPAA regulations. By enforcing strict access controls and logging all data exchanges, they achieved a higher level of data protection and auditability.
3. E-commerce Platform
An e-commerce platform implemented sidecar proxies to enhance observability across their microservices. By integrating with Prometheus, they gained valuable insights into customer behavior and optimized their application performance.
Frequently Asked Questions
1. What is a sidecar proxy?
A sidecar proxy is a design pattern in microservices architecture that runs alongside an application service to manage communication, security, and observability.
2. How do sidecar proxies improve security?
Sidecar proxies enhance security by enforcing encryption, managing authentication, and centralizing policy enforcement.
3. Can sidecar proxies help with observability?
Yes, sidecar proxies improve observability by aggregating logs, collecting metrics, and enabling distributed tracing.
4. What are some popular sidecar proxies?
Popular sidecar proxies include Envoy, Istio, and Linkerd.
5. How do I implement a sidecar proxy?
To implement a sidecar proxy, choose the right proxy, define security policies, monitor performance, and incorporate CI/CD practices.
6. Are sidecar proxies suitable for all applications?
While sidecar proxies are beneficial for microservices, they may not be necessary for simpler architectures.
7. What is the difference between a sidecar proxy and an API gateway?
A sidecar proxy operates at the service level, while an API gateway manages traffic between clients and services.
8. How do sidecar proxies impact application performance?
Sidecar proxies can introduce some latency, but their benefits in security and observability often outweigh the performance costs.
Conclusion
In conclusion, sidecar proxy patterns represent a powerful strategy for enhancing security and observability in cloud containers. By decoupling ancillary functionalities from application logic, organizations can implement robust security measures and gain valuable insights into their microservices. As cloud environments continue to evolve, adopting sidecar proxies will be key to maintaining operational excellence and ensuring compliance. For enterprises looking to leverage cloud infrastructure effectively, consider integrating sidecar proxies into your architecture for improved security and observability.